

Deliver Events to a Syslog Receiver
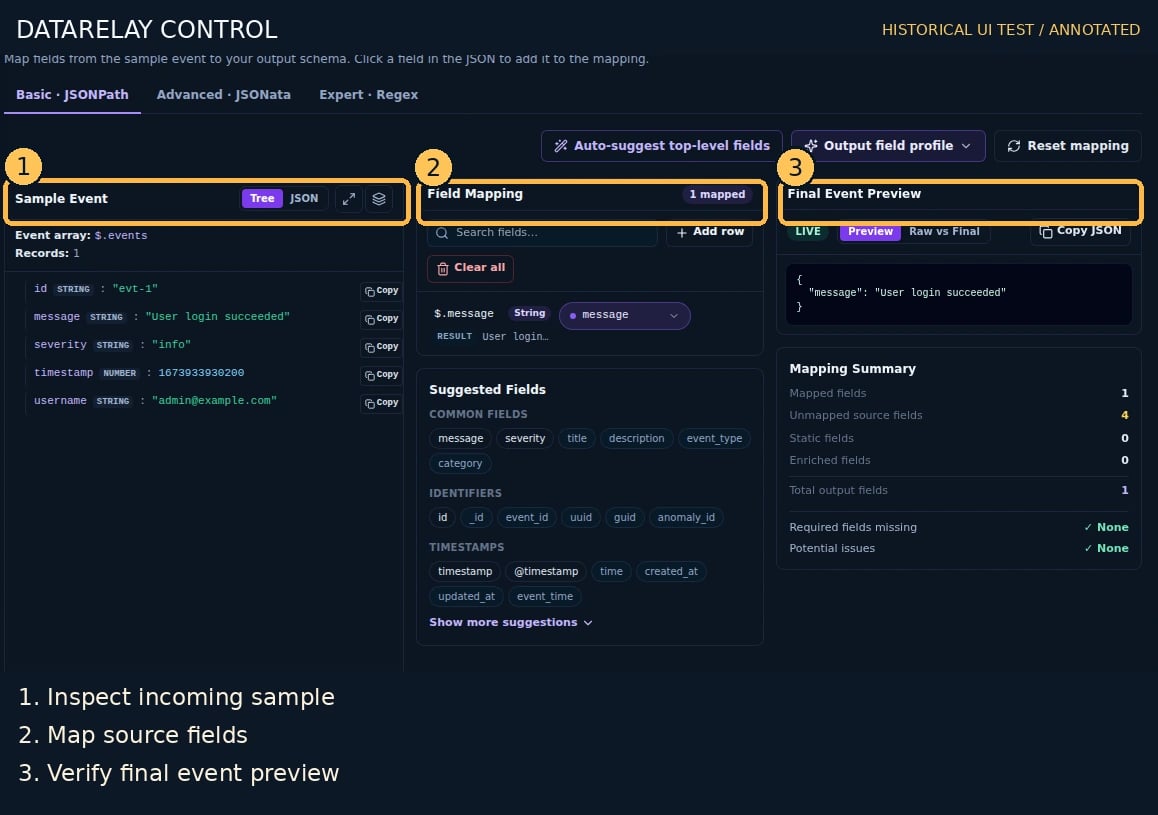
Goal: send one synthetic event to an independently monitored Syslog UDP listener. SYSLOG_TCP and SYSLOG_TLS are available as other Destination types, but this walkthrough deliberately exercises UDP only.Screen version: The numbered images are historical Control UI test captures. Follow the current five-step flow (Connect → Sample & Record Selection → Destinations → Route Processing → Deploy), not older step ordering. See the numbered screenshot guide.
When to use this scenario
This scenario builds on an existing Connector, Destination and Stream. If you have not configured a Source yet, start from the connector-specific collection guides. Follow the concrete steps below and verify actual Logs and Destination/quarantine evidence. Existing test screenshots are illustrative, not runtime proof.1. Prepare the receiver
Run this Python standard-library listener on a test host reachable by the Control server:127.0.0.1 by assumption.
2. Configure the Syslog Destination
- Open Destinations → Create (
/destinations). - Set Name =
Lab Syslog UDP, Type =SYSLOG_UDP. - Set Host to the actual receiver IP and Port =
5514. Save. - Confirm destination and protocol in the list. A saved Destination is not proof of UDP delivery.
3. Create the data flow
- Use the Webhook Receiver Connector with a synthetic event such as
{"id":"syslog-001","message":"hello syslog","severity":"low"}. - Open
/streams/newand complete Connect → Sample & Record Selection with nonzero extracted records. - Choose
Lab Syslog UDPunder Destinations. - In Route Processing, keep a basic Transform, inspect the Route delivery settings and format preview if available.
- Resolve blocking Deploy findings, save/deploy and enable/start the Stream as needed.
4. Send, observe and verify
If it fails
- No datagram: check UDP firewall, container network, receiver listening address, Host/Port, Route enabled state.
- Logs show success but SIEM has no indexed event: debug SIEM parser/indexing separately; UDP success is not SIEM acceptance.
- Need TLS: use
SYSLOG_TLS, valid trust chain and hostname verification; do not use this plaintext UDP example for protected production records.